Cyber attackers are increasingly pivoting toward public blockchains to secure a strategic advantage over digital defenders, utilizing the technology’s inherent censorship resistance to host malicious infrastructure that is nearly impossible to dismantle. According to a comprehensive investigation by Chainalysis, a surging number of threat actors—ranging from financially motivated cybercriminals to state-sponsored agents from Iran and North Korea—are adopting a technique known as "blockchain dead drops" (BDDs). This method involves storing malicious payloads, command-and-control (C2) configurations, and infrastructure pointers directly within on-chain transactions and smart contracts. Unlike traditional centralized servers, which can be seized by law enforcement or taken offline by hosting providers, the permanence of the blockchain ensures that these campaigns remain durable and accessible to infected devices around the clock.

The primary threat posed by blockchain dead drops is not necessarily an increase in destructive power, but rather a significant leap in campaign longevity. By using blockchains as a durable coordination layer, threat actors can survive domain seizures, repository removals, and other common "Web2" disruptions. This shift represents a growing visibility gap in global cybersecurity; traditional threat-intelligence platforms often overlook on-chain activity, allowing malicious communications to persist in the relative obscurity of decentralized networks. As open-source AI coding tools continue to lower the technical barriers for entry, the frequency of BDD-related attacks has skyrocketed, showing a 420% increase over the past 12 months.
The Evolution of Blockchain-Based Evasion
The concept of using decentralized ledgers for malicious purposes is not entirely new, but its complexity and adoption have reached unprecedented levels. The history of BDDs dates back more than a decade, beginning with limited experiments on the Bitcoin blockchain. As early as 2013, a variant of the Necurs botnet began storing C2 domains on Namecoin, a fork of Bitcoin designed for decentralized DNS. By 2019, cybercriminals had refined these methods, encoding C2 IP addresses into the specific amounts of Satoshis (the smallest unit of Bitcoin) being transferred, or writing malicious data into Bitcoin’s OP_RETURN field—a feature intended for embedding small amounts of arbitrary data in the ledger.

A major turning point occurred in mid-2023 with the emergence of "EtherHiding." This technique was pioneered by the operators of ClearFake, who turned to the Binance Smart Chain (BSC) after Cloudflare began cracking down on the servers used to deliver their infostealing malware. By embedding malicious code within smart contracts on BSC, the attackers ensured their campaign could not be taken offline. This success sparked a wave of imitation. By late 2023, the Smargaft DDoS botnet was utilizing BSC-based smart contracts for its C2 operations.
The timeline of adoption suggests a clear progression from experimental criminal use to sophisticated state-level operations. In late 2024, Iranian threat actors linked to the Ministry of Intelligence began embedding C2 data in Bitcoin transactions. By early 2025, North Korean agents adopted EtherHiding to enhance their "fake job interview" ruse, a long-running campaign designed to steal cryptocurrency from developers. Data indicates that malicious writes to the blockchain have surged from an average of 2.06 per day to 11.1 per day—a 440% increase—largely catalyzed by the release of unrestricted, high-capacity open-source AI models in mid-2025.

Technical Mechanics of the Blockchain Dead Drop
Blockchain dead drops function as a modern iteration of traditional espionage "dead drops," where information is left in a public but discreet location for another party to retrieve. In the digital realm, these locations are specific transactions or smart contracts. Chainalysis has identified three primary techniques currently in use by Russian, Iranian, and North Korean actors:
1. Transaction-Based Storage
Threat actors use standard blockchain transactions to publish C2 configurations or payload references. These are often hidden in the "memo" or "input data" fields of a transaction. The malware on the victim’s device is programmed to monitor a specific blockchain address, retrieve the latest transaction, and decode the embedded data to find the current IP address of the attacker’s server. This allows the attacker to rotate their infrastructure frequently; they simply send a new transaction with updated data, and every infected machine automatically updates its connection.

2. Contract-Based Storage (EtherHiding)
This method utilizes the programmable nature of Ethereum Virtual Machine (EVM) chains like BSC and Polygon. Attackers deploy smart contracts that act as resilient storage lockers. The malware queries the contract’s state to retrieve updated instructions. Because the logic is hosted on a decentralized network of thousands of nodes, there is no central authority that can "delete" the contract or block access to it without fundamentally altering the blockchain’s protocol.
3. Phantom Wallet Addressing
A more stealthy and lightweight strategy involves "phantom wallets"—blockchain addresses that do not have a corresponding private key-pair. Attackers hide their C2 server’s IP address within the actual bytes of the wallet address itself. By sending zero-value transactions to these addresses, the attackers create a public record that the malware can scan. The malware is designed to decode the IP address from the phantom destination address and establish a connection off-chain.

Case Studies: Geopolitical Actors and Their Methods
The adoption of BDDs by nation-states highlights the strategic value of blockchain for sovereign cyber operations. Analysis of recent campaigns reveals distinct styles of utilization among different threat groups.
North Korea (DPRK) and Cross-Chain Redundancy
In February 2025, a North Korean-linked group tracked as UNC5342 began using smart contracts to deliver malware to job-seeking crypto developers. This group implemented a sophisticated redundancy system spanning three different blockchains: TRON, Aptos, and BSC. The malware first attempts to retrieve encoded pointers from TRON; if that fails, it queries Aptos. Both paths lead to a specific transaction on BSC containing encrypted malware instructions. This multi-chain approach ensures that even if one or two networks experience disruptions or implement specific filters, the campaign remains operational. The goal remains consistent with the DPRK’s long-term strategy: the exfiltration of digital assets to fund the regime.

Iran and the Bitcoin Pivot
Iranian operators have taken a different approach, utilizing the Bitcoin blockchain’s OP_RETURN field. They send small, functionally meaningless payments to well-known Bitcoin addresses—some even dating back to the era of Satoshi Nakamoto. These addresses serve as permanent, publicly accessible lookup points. By using highly visible, historical addresses as their "dead drop" location, the attackers reduce their own footprint, as the reference address itself has no direct link to the malicious activity.
Russian-Language Malware-as-a-Service (MaaS)
On the Polygon blockchain, Russian-language criminal groups have established a "Malware-as-a-Service" model. A primary operator maintains a fleet of storage contracts, which are then rented out to downstream affiliates. These affiliates run their own individual malware campaigns, but they all rely on the central operator’s blockchain infrastructure to receive C2 updates. Chainalysis has linked these deployer wallets to a wider ecosystem of fraudulent stablecoins and clipboard-hijacking campaigns, illustrating how a single blockchain-based hub can support a massive variety of criminal activities.

Supporting Data and AI Influence
The sudden escalation in BDD activity is inextricably linked to the democratization of advanced technology. The launch of powerful, open-weight Chinese Large Language Models (LLMs) in mid-2025 provided a significant boost to less-experienced threat actors. Unlike many Western AI models that have strict safety guardrails against generating malicious code, these open-weight models allowed users to generate complex smart contract code and C2 logic with ease.
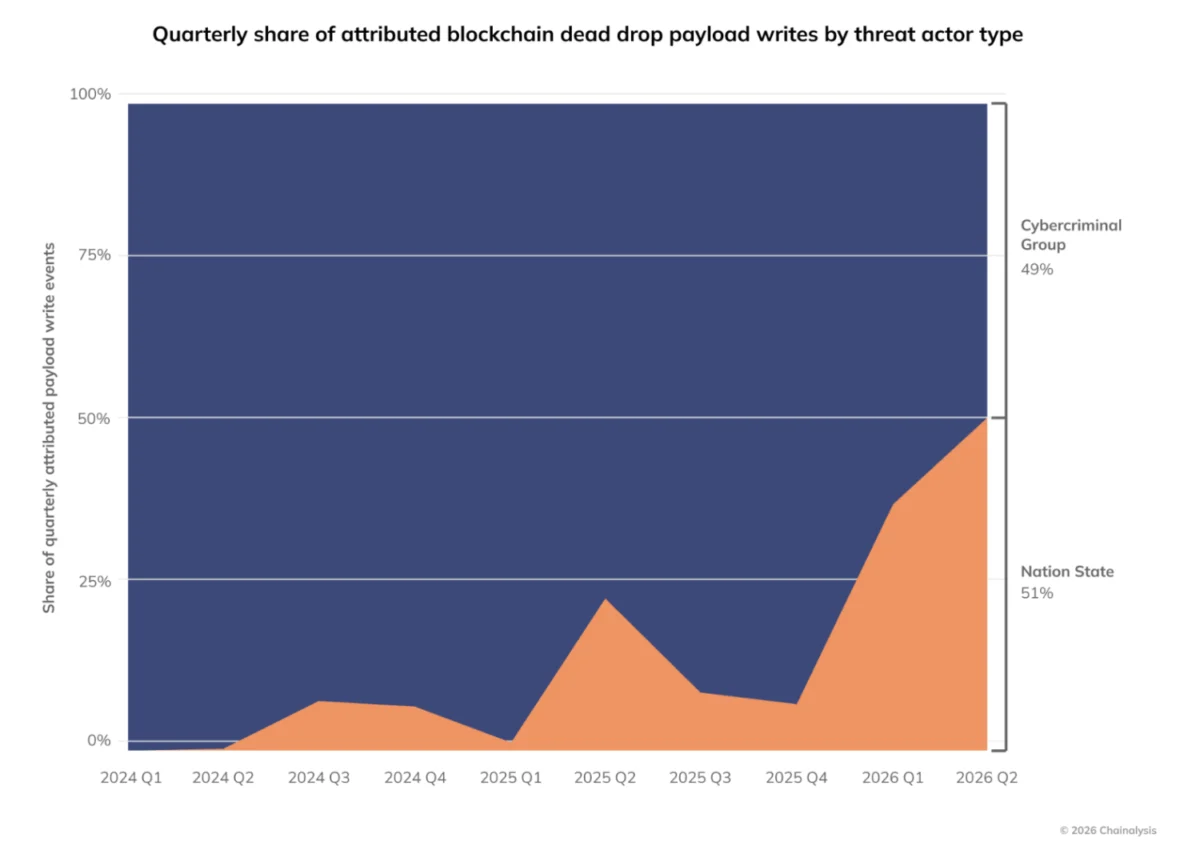
Current metrics show that state-actor-linked groups are now driving the majority of this growth. While cybercriminals accounted for nearly all BDD activity in early 2024, state-linked actors began a rapid ascent in the middle of that year. By the second quarter of 2026, state-sponsored groups were responsible for approximately two-thirds of all new BDD activity per quarter and roughly half of the total cumulative activity on-chain. Currently, Chainalysis is tracking BDD activity across five major blockchains and more than a dozen distinct malware strains.

The Challenge for Global Defense
The inherent nature of public blockchains presents a unique dilemma for cybersecurity professionals. Unlike traditional malicious domains, which can be blacklisted or seized by the FBI or Europol, a smart contract on a decentralized network is immutable.
Industry experts note that blocking "blockchain traffic" at the network level is not a viable solution. Doing so would require blocking public Remote Procedure Call (RPC) endpoints operated by major infrastructure providers like Infura, Alchemy, and Cloudflare. Such a move would effectively break all legitimate blockchain applications, decentralized finance (DeFi) services, and digital wallets within an enterprise environment. Furthermore, sophisticated attackers could easily bypass such blocks by running their own private nodes.

However, the same transparency that makes blockchains attractive to attackers also provides a tool for defenders. Every on-chain update is a permanent, timestamped record. By utilizing blockchain intelligence and infrastructure identification tools, defenders can map out an attacker’s wallet history, funding sources, and update patterns. This allows for "wallet-level attribution," where multiple seemingly unrelated malware campaigns can be traced back to a single operator or state entity.
Broader Impact and Future Implications
The rise of blockchain dead drops signals a shift in the cat-and-mouse game of cybersecurity. As threat actors move away from "brute force" destruction and toward "durable persistence," the metrics for successful defense must also change. The ability of a malware campaign to survive for years without its C2 infrastructure being disrupted poses a long-term risk to financial institutions, government agencies, and individual users alike.

The convergence of AI-driven code generation and decentralized infrastructure suggests that BDDs will become a standard component of the modern cyber-arsenal. For regulators and law enforcement, this necessitates a move toward more integrated blockchain monitoring. For the private sector, it requires a new layer of endpoint visibility that can detect outbound JSON-RPC calls to blockchain endpoints as a potential early warning signal of infection.
As long as public blockchains remain cheap, global, and resistant to central control, they will continue to serve as a sanctuary for malicious code. The challenge for the next generation of digital defenders will be to master the same decentralized tools that their adversaries are currently using to hide in plain sight. Future security frameworks will likely need to incorporate automated on-chain monitoring to preemptively identify the creation of new resolver contracts and transaction patterns associated with known state-sponsored clusters. In this new landscape, blockchain intelligence is no longer just for tracking stolen funds; it is a critical component of national and corporate cyber defense.