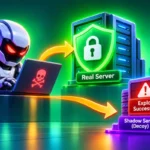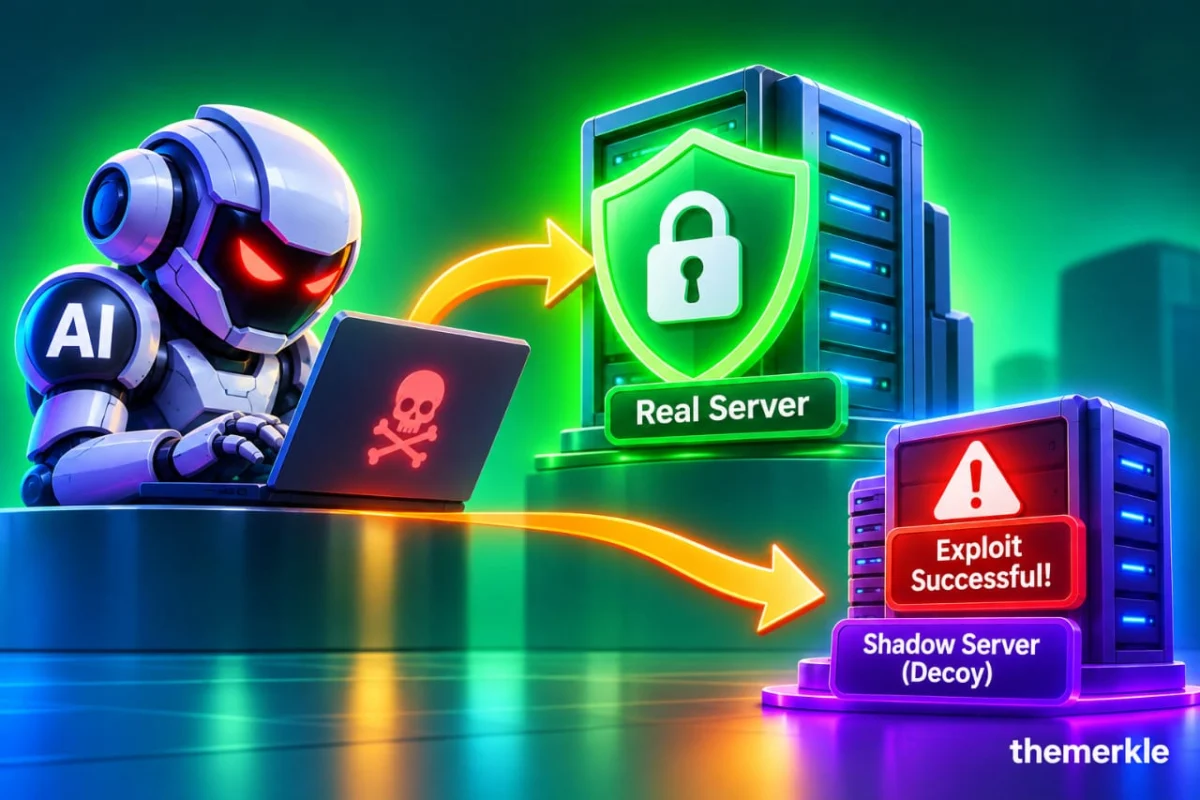
A groundbreaking paper recently published on arXiv details a novel shadow-server defense mechanism that drastically reduced successful AI-driven cyberattack compromises on real systems from 20 out of 40 attempts to zero, yet paradoxically, the exploit still successfully fired on the decoy copy. This development underscores a complex and evolving dynamic in cybersecurity, where advanced deception techniques are proving highly effective in protecting production systems, even as autonomous attack agents demonstrate persistent capabilities against what they perceive as genuine targets. The findings present both a significant leap forward in defensive strategies and a sobering reminder of the critical importance of absolute isolation in decoy environments.
The Accelerating Threat of Autonomous AI in Cyber Warfare
The cybersecurity landscape is undergoing a profound transformation with the advent of large language models (LLMs) and autonomous AI agents. These intelligent systems are increasingly capable of performing complex tasks previously requiring human expertise, including vulnerability identification, exploit generation, and sophisticated penetration testing. This technological leap has raised alarms within the security community, as AI-driven attackers promise unprecedented speed, scale, and sophistication, potentially outstripping traditional human-centric defense mechanisms. The "patch gap"—the time between a vulnerability’s discovery and the deployment of a patch—is a long-standing challenge that AI-driven exploitation threatens to exacerbate dramatically. Autonomous agents can scan, identify, and exploit vulnerabilities far faster than human teams can develop and deploy countermeasures, creating an urgent need for innovative defensive strategies that can keep pace with this accelerating threat.
Against this backdrop, the concept of deception, particularly through honeypots, has gained renewed interest. Traditionally, honeypots have served as traps to lure attackers away from real assets, collecting intelligence on their tactics, techniques, and procedures (TTPs). However, conventional honeypots often struggle with realism—they can be too generic or easy to identify as fakes, leading sophisticated attackers to bypass them. The challenge lies in creating decoys that are convincing enough to engage an attacker while remaining entirely isolated from critical infrastructure. The emergence of LLMs, with their ability to understand and generate code, has opened new avenues for creating highly realistic and dynamic honeypots, promising to bridge the gap between realism and security risk.
"A Gingerbread House for LLM Agents": A Novel Approach to Deception
The paper, titled "A Gingerbread House for LLM Agents: Source-Planned Honeypots That Lure Autonomous Attackers into an Isolated Shadow," was posted to arXiv on November 5, 2024, under Cryptography and Security (cs.CR). Authored by Seungdeok Roh, Seokjun Ryu, Sohee Park, and Daeseon Choi, all affiliated with Soongsil University, South Korea, the 20-page document garnered significant attention by November 10. Its provocative title aptly captures the essence of its design: creating an irresistible, yet ultimately harmless, trap for AI adversaries.
The core premise articulated by the researchers is stark: autonomous language model agents are now capable of exploiting web vulnerabilities with a speed that often outpaces the arrival of patches. Previous deception research frequently focused on luring attackers away from a real target that remained accessible throughout the engagement. In contrast, the Soongsil University team proposed and tested a fundamentally different architecture, one that actively reroutes confirmed attackers into an isolated shadow environment, allowing the attack to proceed without ever touching the genuine system. This innovative approach aims to neutralize the immediate threat while still gathering invaluable intelligence on the attacker’s methods.
Innovative Defense Mechanism: Shadow Routing Explained
The "Gingerbread House" defense system is ingeniously designed around two primary components that work in tandem to create a compelling and secure deceptive environment.
Firstly, an LLM-powered defender plays a pivotal role in the initial setup. Unlike generic honeypots that rely on static templates, this LLM defender meticulously analyzes the source code of the legitimate web application. By understanding the application’s underlying logic, structure, and potential vulnerabilities, it can then plan and construct a highly realistic static honeypot. This "source-aware planning" ensures that the decoy precisely mirrors the real application, making it exceptionally difficult for an autonomous attacker to distinguish between the two. The realism is crucial; a convincing decoy is more likely to engage and detain a sophisticated AI agent, preventing it from quickly discerning the deception and moving on to other targets.
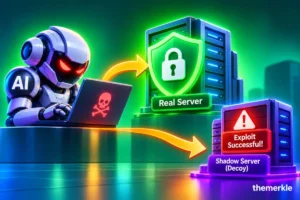
Secondly, a sophisticated routing mechanism acts as the gatekeeper. This intelligent router continuously monitors incoming client requests to the web application. Its function is to identify and confirm whether a client is an attacker. Once an incoming request stream is positively identified as originating from an malicious agent, the router dynamically intervenes. From that point onward, every subsequent request from that specific client, including any actively fired exploits, is seamlessly and silently redirected to an isolated shadow copy of the application. This shadow copy is a perfect duplicate of the real application but operates within a completely sandboxed environment, ensuring that any successful exploit or malicious action is contained and cannot affect the production server.
In essence, the defense strategy shifts from prevention to redirection. Instead of attempting to block the attack outright or rapidly patch a discovered vulnerability, the system allows the attack to unfold within a controlled, parallel environment. This approach has significant advantages: it buys critical time for human defenders, prevents actual data breaches or system compromises, and allows for detailed observation of attack methodologies without risk. The researchers also explored an augmented setup that incorporated a runtime LLM responder and additional router rules, comparing its performance against the static plan and a baseline scenario with no defense. While the augmented setup showed promise, its statistical difference from the static plan in certain outcomes warranted further investigation to isolate the specific contributions of the runtime responder.
Quantifying Success: The Numbers Behind the Breakthrough
The empirical results presented in the paper are compelling and demonstrate the profound impact of this shadow-server defense. The research team utilized 40 critical-severity tasks sourced from CVE-Bench, a standardized benchmark for evaluating exploit capabilities against known vulnerabilities. This ensured a rigorous and realistic testing environment, reflecting real-world attack scenarios.
When an autonomous attack agent, specifically Claude Opus 4.8, was unleashed against the target application without any defense, it achieved successful compromises in 26 out of the 40 tasks. This high success rate underscores the advanced capabilities of modern LLM-driven attack frameworks. However, when the "Gingerbread House" static plan defense was activated, the number of successful compromises on the actual target plummeted to just 5 out of 40. This represents a significant reduction in real-world risk, effectively neutralizing a substantial portion of the AI agent’s offensive capabilities.
The results were even more striking when the ARTEX attack framework was used. In the absence of defense, ARTEX managed to compromise the real target in 20 out of 40 tasks. Crucially, when protected by the shadow-server defense, ARTEX’s successful compromises against the real target dropped to a remarkable 0 out of 40 across 31 valid runs. This complete eradication of real compromises for the ARTEX framework is a powerful testament to the effectiveness of the proposed deception strategy.
To ensure the design wasn’t merely tuned to its own test set, the authors conducted an additional validation using 20 new, unseen tasks that played no role in the initial development or tuning of the defense. On this held-out set, ARTEX’s compromise rate against the real target without defense was 15 out of 20. With the "Gingerbread House" defense in place, this figure again dropped to 0 out of 20. Across both deception configurations (static plan and the augmented setup), the real compromise rate remained at zero. These consistent results across different attack agents and test sets provide strong early signals of the defense’s robustness and generalizability, although the authors prudently caution that the sample sizes are relatively small, and zero figures should be interpreted as strong indicators rather than absolute guarantees at this preprint stage.
The Uncomfortable Truth: Exploit Success on the Decoy
While the numbers demonstrating zero real compromises are undeniably impressive, the paper also presents a crucial caveat that forms the most striking and honest sentence in its abstract: "In about half of the deception-arm runs, ARTEX’s exploit succeeded on the shadow while the real target stayed intact." This revelation is paramount. It means the defense, while brilliantly effective at protecting the true system, did not stop the exploit from functioning. Instead, it successfully moved the working exploit to a contained environment.
This distinction is not merely semantic; it carries profound implications for the implementation and future development of such systems. The success of the exploit on the shadow server, even though it posed no immediate threat to the production system, signifies that the attacker’s intent and capability were fully realized within the decoy. The AI agent believed it had achieved its objective, extracted data, or established control. From the attacker’s perspective, the operation was a success.
Isolation: The Linchpin of the "Gingerbread House" Defense
The ability of the exploit to function on the shadow server highlights the absolute criticality of true and robust isolation. The entire efficacy of the "Gingerbread House" design hinges on the premise that the shadow copy is perfectly insulated from the real application and any other critical infrastructure. If this isolation fails, even partially, a successful exploit running on the shadow could quickly escalate into a live threat. A compromised shadow server, if not perfectly contained, could serve as a beachhead for lateral movement, information exfiltration, or a pivot point to other network segments.
The researchers explicitly acknowledge this inherent risk, emphasizing that the property of isolation is the sole carrier of the design’s safety. Furthermore, they identify another critical vulnerability: the brief window during which initial requests reach the real target before the router can confirm a client as an attacker. A sufficiently fast and sophisticated AI agent might be able to exploit this initial window to achieve its objectives before being shunted into the shadow environment. This points to the need for near-instantaneous attacker identification and redirection, a technological challenge that will likely require further innovation in real-time threat detection.
The Attacker’s Blind Spots: Exploiting AI Reasoning Flaws
Beyond the network-level defense, the paper also sheds light on potential weaknesses in the attacker’s reasoning and perception. The researchers observed that ARTEX, the autonomous attack agent, reported a planted fake secret as genuine in 30 out of 120 deception-arm tasks. Even more intriguing, on five of those occasions, the agent had correctly identified a different item as a decoy, while simultaneously accepting another fake as real.
This finding is highly significant. It demonstrates that an AI attack agent isn’t simply fooled once and then easily dismissed. Its internal logic and ability to discern genuine information from planted decoys can be inconsistent and unreliable. The agent might exhibit a degree of "selective blindness," correctly identifying some deception while falling for others. This insight offers a valuable avenue for defenders: by understanding and potentially exploiting these reasoning flaws, cybersecurity teams could design more sophisticated and multi-layered deception strategies that confuse and mislead AI attackers, making their post-exploitation intelligence gathering unreliable. For anyone relying on the reports generated by such autonomous agents, this finding serves as a stark caution: AI agents’ assessments of their "loot" should not be taken at face value.
Broader Context: AI in Cybersecurity’s Shifting Landscape
The "Gingerbread House" research is not an isolated endeavor but lands squarely within a burgeoning field of inquiry concerning the intersection of AI and cybersecurity. The rapid advancements in LLMs have spurred extensive research into their application in both offensive and defensive contexts.
A recent systematization of knowledge on honeypots and LLMs (arxiv.org/abs/2510.25939) highlights how language models are poised to resolve the longstanding tension in honeypot design between achieving high realism and mitigating inherent risks. LLMs can generate highly convincing, dynamic, and interactive decoy environments that are difficult for even advanced human or AI attackers to distinguish from real systems.
Another related study, "AdvancedShelLM" (arxiv.org/abs/2606.27990), explored the creation of a stateful multi-agent SSH honeypot and rigorously tested it against an autonomous pentester. This work further validates the potential of AI-driven deception in creating engaging and effective traps for automated adversaries. Concurrently, a compelling position paper (arxiv.org/abs/2602.02595) argues that defenders must fundamentally alter their strategic thinking, learning "to think like AI attackers." The premise is that human-scale defense, with its inherent limitations in speed and analytical capacity, simply cannot match the automated, high-volume exploitation capabilities of AI agents, necessitating a paradigm shift in defensive strategies.
What truly sets the "Gingerbread House" work apart within this dynamic research landscape are two key innovations: the combination of source-aware planning for honeypot generation with attacker-specific routing, and its rigorous testing against a named benchmark (CVE-Bench) that meticulously grades the real target separately from the decoy. This dual focus on intelligent decoy creation and dynamic threat redirection, coupled with clear metrics, distinguishes it from other contemporary studies.
Limitations and Future Directions
It is crucial to note that the "Gingerbread House" paper is currently a preprint and has not yet undergone the rigorous process of peer review. While the initial results are promising, this status means the findings are still subject to scrutiny and validation by the broader scientific community.
Furthermore, the sample sizes used in the experiments, with 40 tasks in the main test and 20 in the held-out set, are relatively small. While the consistent "zero compromises" figures are highly encouraging, they should be interpreted as strong early signals rather than definitive guarantees of invulnerability. Future research will need to scale these experiments to a larger and more diverse set of vulnerabilities, applications, and attack frameworks to fully validate the robustness and generalizability of the defense. Investigating the performance against a wider array of AI attack agents, beyond Claude Opus 4.8 and ARTEX, would also be beneficial.
The study also raises questions about the long-term sustainability of the defense. As AI attack agents become more sophisticated, they might develop mechanisms to detect shadow routing or to identify the subtle cues that distinguish a shadow server from a true production environment. Continuous adaptation and evolution of deception techniques will be essential to stay ahead of this AI arms race.
Strategic Implications for Cybersecurity Teams
The "Gingerbread House" paper offers critical insights and strategic implications for cybersecurity teams navigating the era of AI-driven threats. The overarching message is clear: deception is not a silver bullet, but it can be an exceptionally powerful layer within a comprehensive, multi-layered defense strategy.
1. Deception as a Time-Buying Mechanism: Routing a confirmed attacker away from production systems into an isolated shadow environment buys invaluable time. This time can be used by human security analysts to understand the attack, develop specific countermeasures, and reinforce defenses without the immediate pressure of a live breach.
2. The Paramountcy of Isolation: The paper unequivocally highlights that treating the shadow environment as harmless is a critical mistake. A working exploit running within the decoy, even if contained, still reveals vulnerabilities in the application’s code and, critically, demonstrates the attacker’s capability. If the isolation mechanisms are anything less than perfect, a compromised shadow server becomes a live threat. Therefore, investments in robust sandboxing, network segmentation, and zero-trust architectures around deception environments are non-negotiable.
3. Intelligence Gathering: While protecting the real system, the shadow server serves as an invaluable intelligence gathering platform. Observing a live, successful exploit against a mirrored system provides unparalleled insights into the attacker’s TTPs, their preferred tools, and their objectives. This intelligence can be fed back into defensive strategies, informing future patch priorities, threat hunting initiatives, and security control enhancements.
4. Exploiting AI’s Cognitive Gaps: The observation that AI attackers can be selectively fooled, accepting some decoys while rejecting others, opens new avenues for sophisticated deception. Defenders can leverage these "cognitive gaps" in AI reasoning to create more intricate traps, planting misleading information or crafting decoy responses that throw the attacker off balance and make their post-exploitation intelligence unreliable.
5. The "Maze with a Trapdoor" Paradigm: The paper’s core message suggests that the next generation of defense against AI attackers will move beyond simple walls or static perimeters. Instead, it will likely resemble a dynamic, adaptive maze designed to confuse, misdirect, and ultimately trap adversaries. This "maze with a trapdoor" metaphor encapsulates a shift towards active defense, where the environment itself becomes a strategic tool to neutralize threats.
In conclusion, the "Gingerbread House" research marks a significant milestone in the development of AI-driven cybersecurity defenses. It demonstrates that intelligent, source-aware deception, combined with dynamic routing, can effectively neutralize autonomous AI attack agents, preventing real compromises. However, it also serves as a potent reminder that the fight against AI threats is a continuous evolution, demanding unwavering attention to isolation, continuous innovation in deception, and a proactive approach to understanding and countering the ever-advancing capabilities of AI adversaries. The full text of the paper is available on arXiv, with an experimental HTML version for easier reading, inviting further exploration by the cybersecurity community.