Ledger, a leading provider of hardware cryptocurrency wallets, is currently investigating a significant security incident involving over $86 million in reported cryptocurrency losses. The thefts primarily affect users in Southeast Asia who acquired their Ledger hardware wallets through an authorized reseller, CryptoBilis. Preliminary findings suggest that the compromised devices may have been counterfeit or tampered with before reaching customers, rather than indicating a fundamental vulnerability in Ledger’s broader product line. As a direct response to the unfolding situation, Ledger has instructed CryptoBilis to immediately suspend all sales and shipments of its products while the investigation remains ongoing.
The incident underscores a critical vulnerability point in the cryptocurrency ecosystem: the supply chain for hardware security devices. While hardware wallets are widely lauded for their ability to keep private keys offline and secure from internet-based attacks, their integrity hinges entirely on the authenticity and untampered nature of the physical device. If a device is compromised at any point between manufacturing and reaching the end-user, the fundamental security premise of cold storage is undermined, potentially exposing digital assets to sophisticated theft.
Unraveling the Multi-Chain Heist: An On-Chain Analyst’s Perspective
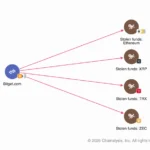
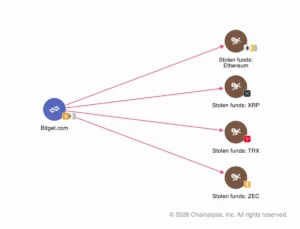
The scale and nature of the theft came to prominence following reports across social media platforms, including X (formerly Twitter) and Reddit, from users detailing inexplicable draining of their crypto wallets. On-chain analyst Specter played a crucial role in bringing the scope of the incident to light, meticulously tracing the flow of stolen funds across multiple major blockchain networks. Specter’s analysis identified inflows from hundreds of victim wallets into specific theft addresses on Ethereum, TRON, and Bitcoin.
The identified theft addresses include Bitcoin addresses beginning with ‘bc1q’, TRON addresses starting with ‘T’, and Ethereum addresses commencing with ‘0x’. This cross-chain activity highlights the sophisticated nature of the attack, demonstrating the perpetrators’ ability to manage and consolidate stolen assets across disparate blockchain ecosystems. The aggregate losses identified by Specter’s analysis quickly surpassed $86 million, a staggering sum that immediately drew widespread attention within the cryptocurrency community.
Specter’s findings, shared publicly, strongly suggested a localized supply chain attack involving a specific reseller. This distinction is vital, as it differentiates a targeted compromise of distribution channels from a systemic vulnerability within Ledger’s proprietary hardware or firmware. The evidence, according to Specter, pointed away from a broad flaw in Ledger devices themselves and towards an issue with how certain devices were procured and distributed to end-users.
Immediate Reactions and Warnings from Industry Leaders
The gravity of the situation prompted swift reactions from prominent figures in the crypto industry. Changpeng Zhao (CZ), the founder of Binance, one of the world’s largest cryptocurrency exchanges, issued a public warning to users. CZ advised caution for anyone who had recently purchased a Ledger hardware wallet, particularly reiterating the assessment that the incident appeared to be a localized supply chain attack involving a single vendor. He emphasized that a "small number of people probably bought fake (or tampered) Ledgers," urging users to be vigilant.
CZ’s intervention served to amplify the warning and guide users on immediate precautionary measures. His statement, while cautious, reinforced the narrative that the core Ledger technology was not the source of the vulnerability, thereby helping to manage broader market panic that could have arisen from perceptions of a widespread hardware wallet compromise. The collective message from analysts and industry leaders was clear: the threat vector was the integrity of the physical device before it reached the user, not a flaw in its operational security once properly set up.
Understanding Supply Chain Attacks on Hardware Wallets
Hardware wallets are designed with multiple layers of security, including secure elements, proprietary firmware, and rigorous authentication processes during setup. The core principle is that the private keys, which control access to cryptocurrency, never leave the device and are never exposed to an internet-connected computer. This "air gap" protection makes them highly resistant to online hacking attempts.
However, this robust security model is predicated on the assumption that the device itself is genuine and has not been physically or digitally altered. A supply chain attack exploits this critical point of trust. Such an attack could manifest in several ways:
- Counterfeit Devices: Attackers could manufacture or procure non-genuine devices that mimic Ledger’s appearance but contain malicious hardware or firmware designed to steal private keys or recovery phrases.
- Tampering with Genuine Devices: Authentic Ledger devices could be intercepted during shipping or storage, opened, modified with malicious components (e.g., chips, firmware), and then resealed to appear legitimate. This could involve installing malware that generates compromised recovery phrases or transmits them to attackers.
- Pre-seeded Recovery Phrases: In some cases, tampered devices might present users with a recovery phrase that has already been known to the attackers, or prompt the user to enter their own recovery phrase into a malicious interface.
The key challenge for users is that sophisticated tampering can be incredibly difficult to detect. Genuine Ledger devices come with specific security seals and rigorous initial setup procedures designed to verify authenticity. However, determined attackers can replicate packaging and seals, making visual inspection insufficient. This incident highlights the paramount importance of users purchasing hardware wallets directly from the official manufacturer or highly reputable, verified distributors with established security protocols.
Ledger’s Ongoing Investigation and Collaborative Efforts
Ledger’s immediate instruction to CryptoBilis to halt sales and shipments is a critical precautionary step. This action aims to prevent any further potentially compromised devices from reaching customers while the full scope of the breach is determined. The company’s investigation will focus on several key areas:
- Compromise Method: Precisely determining how the devices were tampered with or counterfeited. This could involve forensic analysis of affected devices.
- Scale of Impact: Ascertaining the exact number of users affected, the total value of lost funds, and the geographical spread beyond Southeast Asia.
- CryptoBilis’s Role: Investigating the reseller’s supply chain, storage, and distribution practices to identify the point of compromise.
- Recovery Potential: Exploring avenues for tracing and potentially recovering stolen assets through collaboration with exchanges, law enforcement, and on-chain analytics firms.
The incident highlights the critical role of blockchain analysis in modern financial crime. Specter’s ability to trace funds across multiple networks provides investigators with invaluable leads. CZ’s expectation that "industry participants help trace and recover the assets" underscores the collaborative spirit often seen in crypto security incidents, where exchanges, analytics firms, and wallet providers work together to identify culprits and potentially freeze stolen funds when they hit centralized platforms.
Implications for Cryptocurrency Users and the Industry
This $86 million theft serves as a stark reminder of the multifaceted security challenges inherent in the cryptocurrency space. For individual users, the primary takeaways are:
- Source Matters: Always purchase hardware wallets directly from the manufacturer’s official website or from highly trusted, established retailers. Avoid third-party resellers, especially those with unverified reputations or unusually low prices.
- Verify Authenticity: Upon receiving a hardware wallet, meticulously inspect the packaging for any signs of tampering (broken seals, signs of re-taping, inconsistencies). Follow the manufacturer’s specific instructions for device verification, which often involve cryptographic checks during the initial setup process. Never use a device that appears to have been opened or tampered with.
- Secure Setup: Never use a pre-generated recovery phrase provided with a device. Always generate a new recovery phrase on the device itself and store it securely offline. Do not take photos of it, store it on a computer, or share it with anyone.
- Beware of Phishing: Be highly suspicious of any software or websites that ask you to enter your existing recovery phrase. Hardware wallets are designed so that the recovery phrase is only entered directly onto the device during initial setup or recovery, never into a computer.
- Regular Security Audits: Periodically review your security practices, ensure your device’s firmware is up to date (only through official channels), and consider diversifying your holdings across multiple security solutions.
- What to Do if Compromised: If you suspect your Ledger device has been compromised, immediately move your assets to a new, verified secure wallet. Contact Ledger support for guidance and report the incident to relevant authorities.
For the broader cryptocurrency industry, the incident carries several implications:
- Enhanced Supply Chain Scrutiny: Manufacturers like Ledger may need to implement even stricter controls over their distribution networks, potentially reducing reliance on third-party resellers or implementing more robust authentication mechanisms for physical devices.
- Reseller Accountability: The incident will likely lead to increased scrutiny of reseller networks, prompting calls for greater transparency and accountability from all entities involved in the distribution of critical security hardware.
- Education and Awareness: There’s a renewed need for user education campaigns emphasizing the risks of supply chain attacks and best practices for purchasing and verifying hardware wallets.
- Collaboration Against Crypto Crime: The incident highlights the growing sophistication of crypto thieves and the continued necessity for strong collaboration between blockchain analytics firms, exchanges, wallet providers, and law enforcement agencies to trace, freeze, and recover stolen assets.
- Regulatory Focus: Such high-value thefts could attract further attention from financial regulators globally, potentially leading to calls for stricter consumer protection measures in the crypto hardware market.
Historical Context: A Persistent Threat
While this specific incident involves Ledger and a reseller, supply chain attacks and device tampering are not entirely new to the cryptocurrency world. In the early days of crypto, some users reported receiving hardware wallets that had pre-seeded recovery phrases or had been tampered with to drain funds. These incidents, though less frequent and often smaller in scale, have historically underscored the vulnerability inherent in trusting the physical integrity of a device acquired through unofficial channels. The sheer volume of this latest theft, however, marks it as one of the most significant supply chain compromises in recent memory, particularly concerning a major hardware wallet brand.
The ongoing investigation by Ledger will be crucial in providing definitive answers regarding the exact nature of the compromise, the number of victims, and any potential for asset recovery. For now, the crypto community remains on high alert, reinforcing the timeless adage in cybersecurity: trust but verify, especially when it comes to the physical security of your digital assets. The distinction between a localized supply chain issue and a systemic vulnerability is critical, but for affected users, the outcome is the same: significant financial loss, underscoring the constant need for vigilance and adherence to best security practices.