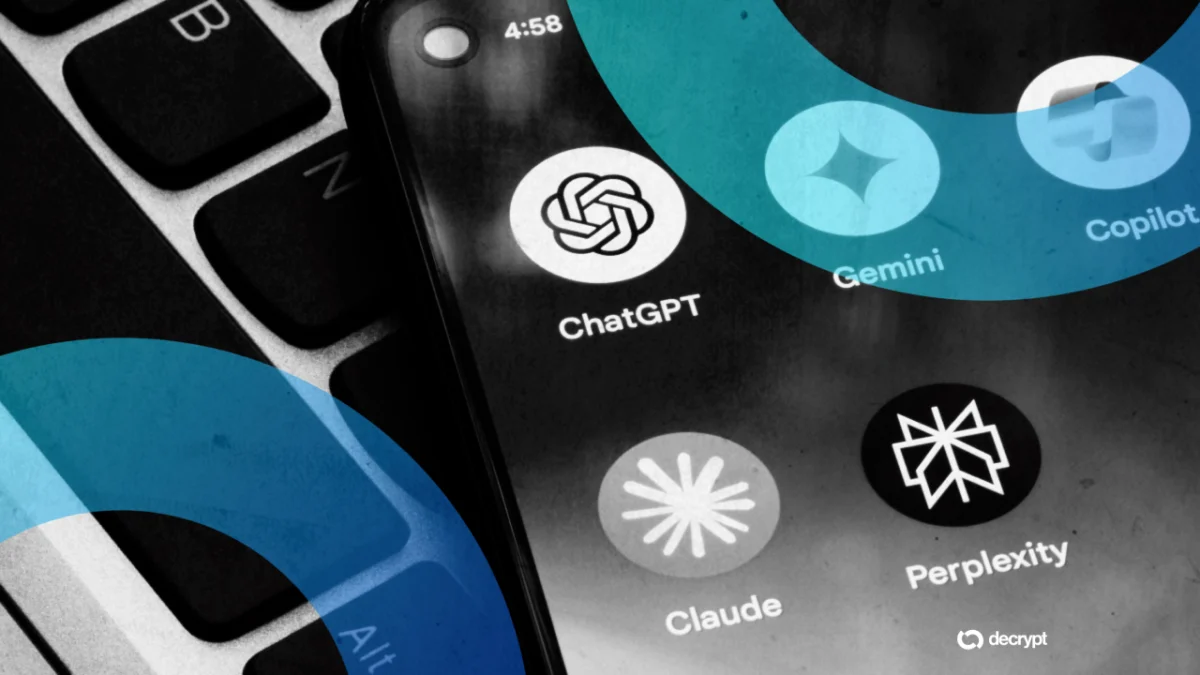
Effective Monday, Sweden’s Government Offices, the critical administrative body providing support to the Prime Minister and the entire cabinet, has instituted a comprehensive ban on the use of popular generative artificial intelligence tools, ChatGPT and Claude, across all staff computers. This directive mandates that civil servants are to exclusively use Microsoft’s Copilot as the sole approved AI application for official duties. The move, first reported by Sweden’s national public broadcaster Sveriges Radio, signals a growing caution among governmental bodies regarding the integration of rapidly evolving AI technologies within sensitive public sector operations.
The Rationale Behind the Ban: Information Security at the Forefront
The impetus for this decisive action stems directly from profound concerns regarding information security. Mikael Wettercrantz, the Government Offices’ director of digitalisation, articulated the rationale in a statement circulated on the staff intranet, highlighting the inherent risks associated with employing AI services that lack formal contractual agreements. "Using AI services without a formal contract can have consequences for our information security," Wettercrantz cautioned, underscoring the potential vulnerabilities such practices could introduce into the government’s digital infrastructure.
Wettercrantz elaborated on these concerns, stating, "We have seen several examples of problematic use of open AI services. The examples concern both the sensitivity of the information that has been entered and how the AI-generated responses have been handled." This statement points to a dual threat: the inadvertent exposure of classified or sensitive governmental data through user inputs, and the potential for AI-generated outputs to contain inaccuracies, biases, or even security risks if not properly managed and verified. The core issue lies in the fact that many consumer-grade AI tools, including ChatGPT and Claude in their standard configurations, transmit user queries to external company servers. Without explicit, legally binding formal agreements, these companies operate under their own terms of service, which may permit broad data collection, processing, and even, in some jurisdictions like the United States, compel data handover to authorities upon request under acts such as the CLOUD Act.
A formal security agreement, in contrast, meticulously defines the parameters of data handling, stipulating what the AI service provider can and cannot do with the inputs from government employees. Such contracts typically include provisions for data residency (where data is stored), data anonymization or pseudonymization, strict access controls, and adherence to specific data protection regulations. This critical distinction between a thoroughly vetted enterprise contract and an open consumer tool is the cornerstone of Sweden’s new policy.
Microsoft Copilot: The Approved Alternative and Its Security Framework
Microsoft Copilot’s approval by the Swedish Government Offices was not granted without rigorous scrutiny. The administrative body conducted a comprehensive review of Copilot’s security architecture and privacy policies. Following this assessment, the Government Offices worked to enhance Copilot’s security settings to meet their stringent requirements, a level of due diligence that was not undertaken for ChatGPT or Claude. This tailored approach suggests that while the underlying AI models might be powerful, the critical factor for government adoption is the surrounding legal and technical framework governing data interaction.
It is important to note, however, that the ban is not absolute for all employees. A limited number of civil servants retain access to both ChatGPT and Claude through an AI platform developed internally by the Government Offices. The precise number of individuals with this privileged access and the specific restrictions applied to their usage have not been publicly disclosed by the press office. This tiered access indicates an acknowledgment of the potential benefits of these tools for specific, controlled applications, while maintaining an overarching policy of caution for general use.
A Broader Trend: Sweden and Europe’s Evolving AI Governance

Sweden’s decision is not an isolated incident but rather a significant marker in a broader European and global trend towards more stringent governance of AI in the public sector. Concerns about data security, privacy, and algorithmic transparency have been steadily mounting since early 2023.
- Early European Precedents: Italy’s data protection authority notably imposed a temporary ban on ChatGPT in March 2023, citing violations of GDPR (General Data Protection Regulation) related to data processing and age verification. This landmark decision sent ripples across Europe, prompting other data protection agencies to initiate their own investigations into generative AI services.
- Other Swedish Agencies Follow Suit: Within Sweden, several other key public agencies had already moved to implement similar restrictions. The Swedish Tax Agency (Skatteverket) and the National Board of Institutional Care (Statens institutionsstyrelse – SiS) had previously imposed bans on consumer AI tools, reflecting a shared understanding of the risks. The Enforcement Authority (Kronofogden), responsible for debt collection and enforcing court orders, is reportedly in the process of formulating its own decision regarding AI tool usage, further illustrating the widespread nature of these concerns across critical governmental functions.
- Transport Administration Audit: An internal audit conducted at the Swedish Transport Administration (Trafikverket) revealed a concerning situation: approximately ten different AI services were being utilized in what was described as a "widespread and risky way." This finding underscores the challenge government bodies face in controlling the adoption of new technologies by employees eager to leverage their potential, often without full awareness of the associated security protocols or lack thereof.
- European Parliament’s Stricter Stance: The European Parliament, in February, took an even more stringent approach, disabling all AI features across its work devices, including ChatGPT, Claude, and notably, Copilot. The Parliament’s rationale was that it could not guarantee the security of data processed by any of these tools, reflecting a maximalist approach to data protection within its highly sensitive operational environment. This contrasts with Sweden’s current policy, which sanctions one U.S. tech company’s product while blocking others, drawing a narrower line than Brussels.
The European Regulatory Landscape and Digital Sovereignty
These governmental actions are unfolding against the backdrop of an increasingly robust European regulatory framework for artificial intelligence. The EU’s General Data Protection Regulation (GDPR), enacted in 2018, remains a cornerstone of data privacy, imposing strict rules on how personal data is collected, processed, and stored. Generative AI tools, by their very nature, often involve the processing of vast amounts of data, including potentially sensitive information, making compliance with GDPR a paramount concern for European public bodies.
Furthermore, the European Union is on the cusp of implementing the Artificial Intelligence Act, a groundbreaking piece of legislation that aims to regulate AI systems based on their risk level. While the Act primarily focuses on the deployment of AI in critical sectors and high-risk applications, its underlying principles of transparency, fairness, and accountability are already influencing how governments approach AI adoption. The emphasis on digital sovereignty – the idea that nations should have control over their own data and digital infrastructure – also plays a significant role. Relying on foreign-owned and operated AI services, especially those subject to extra-territorial laws like the U.S. CLOUD Act, can be perceived as a compromise to this sovereignty.
The Copilot-Claude Nuance: A Closer Look at Technicalities
A critical technical detail adds a layer of complexity to Sweden’s decision. Microsoft incorporated Anthropic’s Claude models into its Copilot service in early 2026. In the European Union, where Sweden is located, Anthropic’s models within Copilot are designed to be "off" by default, requiring administrators to deliberately enable them.
Sweden’s Government Offices has not publicly confirmed whether its specific instance of Copilot has the Claude models switched on. This technical ambiguity means that the distinction between the "banned" AI (Claude) and the "approved" one (Copilot) might not be as clear-cut as the initial announcement implies. If Claude models are indeed enabled within the approved Copilot instance, it raises questions about the thoroughness of the security review or the specific contractual terms negotiated with Microsoft regarding the use and data handling practices of these integrated models. It underscores the intricate nature of AI supply chains and the challenge of establishing clear boundaries when different models are bundled within a single product.
Implications and Future Outlook
The decision by Sweden’s Government Offices carries several significant implications:
- Reinforced Focus on Data Security: It solidifies the message that robust data security and privacy protection are non-negotiable prerequisites for AI adoption in public administration. This will likely push AI vendors to develop more secure, transparent, and auditable enterprise-grade solutions specifically tailored for governmental use.
- Impact on Digital Transformation: While aiming to secure operations, such bans could initially slow down the broader adoption of AI tools within the government, potentially impacting productivity gains that other sectors might realize. However, it also encourages a more strategic, controlled, and ultimately safer integration of AI.
- Vendor Selection and Market Dynamics: The approval of Microsoft Copilot underscores the importance of established enterprise vendors with a proven track record in security and existing contractual relationships with governments. This could give companies like Microsoft a significant advantage in the public sector AI market.
- The Evolving Role of IT Departments: Government IT and cybersecurity departments will play an increasingly central role in evaluating, deploying, and managing AI tools, moving beyond traditional software procurement to deep dives into data flows, algorithmic transparency, and compliance.
- A Precedent for Other Nations: Sweden’s move, particularly its nuanced approach compared to the European Parliament, offers a model for other nations seeking to balance innovation with security in the public sector. It demonstrates that a complete ban isn’t the only option, but a highly controlled and formally contracted approach is essential.
- The Challenge of Shadow IT: The Transport Administration’s findings on "widespread and risky" AI use highlight the ongoing challenge of "shadow IT," where employees adopt tools without official sanction. This necessitates not just bans, but also comprehensive training, clear guidelines, and provision of approved, user-friendly alternatives.
In conclusion, Sweden’s Government Offices’ decision to block ChatGPT and Claude while endorsing Microsoft Copilot marks a pivotal moment in the ongoing global dialogue about AI governance within sensitive public sector environments. It clearly prioritizes information security and contractual clarity over the immediate widespread adoption of consumer-grade AI tools. As AI technology continues its rapid advancement, governments worldwide will undoubtedly face similar dilemmas, necessitating careful consideration of security, privacy, and national sovereignty in their pursuit of digital transformation. The evolving landscape demands not just technological innovation, but also robust policy frameworks and continuous vigilance to safeguard sensitive information and maintain public trust.